

AI & API Governance
Connect AI and APIs.Without compromise.
AI and API governance purpose-built for healthcare — one place to control how every agent, app, and API reaches the data you’ve already connected.
The challenge
AI is multiplying. Your approach to control needs to scale.
CHAI and Joint Commission guidance helps health systems establish responsible AI practices. Putting that guidance into practice means translating your policies into controls over how AI agents access healthcare data and services.
As new agents and applications come online, you need to know what they’re accessing, what they’re allowed to do, and whether they stay within those boundaries, with a record of activity to support oversight.
Our point of view
Access and control shouldn’t be a trade-off
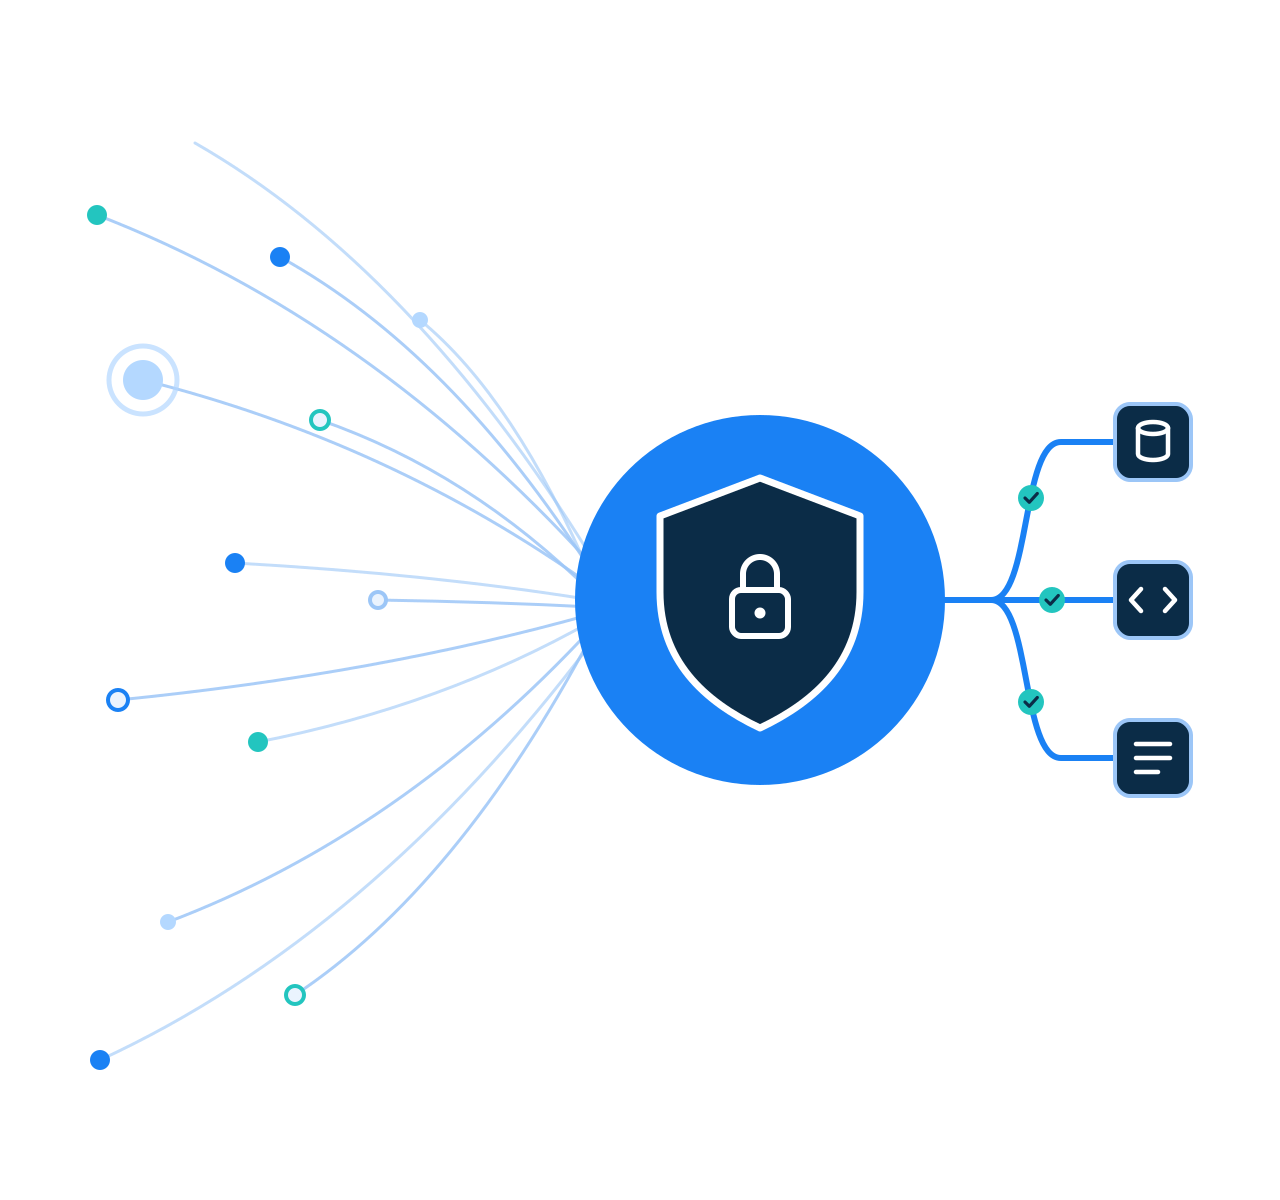
Useful AI needs access to real systems and services. Healthcare organizations need confidence that access stays within the boundaries they set. Rhapsody® Guardian puts those decisions into practice, enforcing access policies as requests occur.
Rhapsody® Guardian
Turn approved access into enforced access
Manage how applications and AI agents reach your healthcare services. Guardian applies controls at the point of access, giving your team a consistent way to authenticate requests, enforce permissions, and review activity.
Configure access
Set up callers and define the services and API operations each caller is permitted to access.
Authenticate and enforce
Guardian verifies the caller and checks incoming requests against configured policies. Requests outside the permitted rules are blocked.
Monitor and review
Review traffic and enforcement records to investigate requests and adjust access policies as requirements change.
FROM POLICY TO PRACTICE
See what passes and what’s blocked
Authorize an agent to access a designated service, restrict it to permitted operations, and limit how frequently it can make requests. Guardian enforces these boundaries and maintains an audit trail of activity passing through it.
Top AI connections
| Connection | Type | Tokens |
|---|---|---|
| DataHeart | Agent · MCPVendor | 22.2M |
| patient-notes-summarizer | App | 17.6M |
| claims-copilot | AppAgent · MCP | 14.8M |
| triage-assistant | Agent · MCP | 12.0M |
Top API connections
| Connection | Type | API calls |
|---|---|---|
| DataHeart | Agent · MCPAPI | 512K |
| Acme Health EHR | VendorAPI | 388K |
| MediSync Partner | VendorAPI | 271K |
| ClaimStream | VendorAPI | 203K |
Policy: permitted FHIR read operations only · Rate limit: enforced · Activity: recorded per request


Over 1,900 customers served

Trust and Compliance
Data security is patient safety
Rhapsody® health solutions are trusted by 1,900+ healthcare organizations around the world, in part because of our commitment to data privacy and security. We have experience complying with complex regulations around the world. In addition to HIPAA and GDPR, there are country-, region-, provincial-, and state-specific regulations and certifications that we stay on top of to ensure compliance for ourselves and our customers.
soc 2 type II
AICPA Service Organization Controls

uk Essential Plus
UK government-backed certification

hitrust csf
Certified for healthcare information security

iso 27001
Certified by A-LIGN
HIPAA • GDPR • PLUS REGIONAL AND STATE-SPECIFIC PROGRAMS
See how Guardian controls AI and API access
Explore where Guardian fits in your environment, which access controls you can apply, and how your team can monitor requests across the connections it governs.